Key Takeaways:
- Siloed Teams Are Your Hidden Multi-Cloud Cost: Federal and state agencies gain flexibility with multi-cloud adoption, but fragmented CloudOps, security, and compliance teams create duplicated effort, delayed authorizations, and governance bottlenecks that compound across every stage of the cloud lifecycle.
- Multi-Cloud Environments Increase Complexity: Each cloud provider doesn't simply introduce another platform; it expands the attack surface and requires updates to security controls, ATO packages, and monitoring strategies. In multi-cloud environments, managing separate control models, compliance requirements, and governance processes transforms manageable complexity into exponential friction.
- Integration Is the Path Forward—and Already Underway: The better approach treats CloudOps, security, and compliance as an integrated system where security is built into design from the start, authorization is continuous, and all functions share visibility and data. Agencies across the federal and state landscape are already making this practical shift to a mission-centered model.
Civilian agencies are under pressure to modernize while preparing for AI-enabled mission delivery. Multi-cloud has become an important part of that strategy, but adopting multiple clouds is only the beginning. Operating it effectively requires an integrated foundation that many agencies are still working to build.
Today's mission environments demand systems that reduce risk from the start and adapt as requirements evolve. That expectation has exposed a challenge: Cloud Operations (CloudOps) teams build and manage cloud services. Security teams implement and monitor controls to protect them. Compliance and Authority to Operate (ATO) teams assess whether those controls meet policy requirements and formally authorize the system to operate. But rather than working as an integrated team, they function as three independent workstreams.
This misalignment compounds quietly across every stage of the cloud lifecycle, leading to duplicated effort, delayed ATO decisions, rework triggered by late-stage risk findings, inconsistent financial management actions and timing, and governance structures that slow decisions instead of enabling them.
Multi-Cloud Makes Existing Gaps Hard to Ignore
Every new cloud service provider an agency adopts introduces more than another platform to manage. It expands the attack surface and materially changes the underlying security architecture.
That shift requires updates to security control implementations, revisions to the ATO package, and adjustments to the continuous monitoring strategy. Meanwhile, each cloud service provider brings its own control models, compliance requirements, operational tooling, and governance processes. Even when providers align to federal frameworks, control inheritance and implementation can differ in meaningful ways.
In a single-cloud environment, complexity is manageable. In multi-cloud, however, complexity does not simply increase; it multiplies.
How Siloed Operations Look in Practice
As they adopt multi-cloud, agencies across the federal and state landscape are navigating a common set of challenges that stem directly from this fragmented operating model.
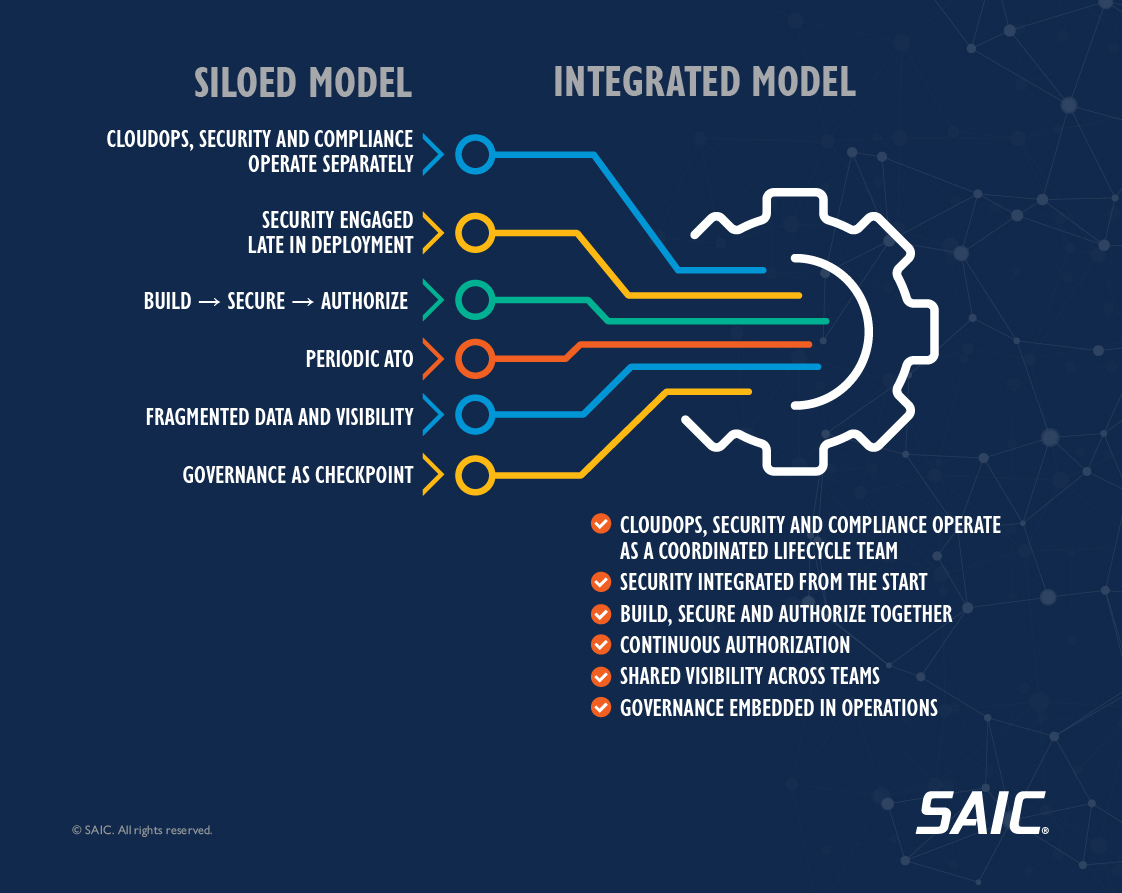
Security engaged late in the lifecycle.
In many organizations, cybersecurity still operates independently from cloud architecture and DevSecOps pipelines. Security reviews often occur after key deployment decisions have already been made. Findings surface late, triggering rework, delays, and inconsistent enforcement of security baselines. Instead of helping shape the architecture from the beginning, security is often forced into the role of catching problems after decisions have already been made.
ATO processes built for static systems.
Traditional ATO processes were designed for a slower pace of change, and annual or milestone-based reviews made sense when systems were relatively static. That isn’t the case in a multi-cloud environment, where configurations change daily and new services are spun up continuously. The issue isn’t the Risk Management Framework itself. It’s the absence of modular ATO processes, reusable control implementation, and automated evidence collection that support ongoing authorization rather than periodic reassessment.
Limited and inconsistent visibility.
Traditional ATO processes were designed for a slower pace of change, and annual or milestone-based reviews made sense when systems were relatively static. That isn’t the case in a multi-cloud environment, where configurations change daily and new services are spun up continuously. The issue isn’t the Risk Management Framework itself. It’s the absence of modular ATO processes, reusable control implementation, and automated evidence collection that support ongoing authorization rather than periodic reassessment.
Governance as a bottleneck.
When risk data is fragmented, routine decisions require reconciliation across multiple stakeholders. Approvals that should be straightforward become extended coordination exercises. Governance becomes another approval step instead of an integrated part of delivery, slowing decisions and encouraging workarounds that create even more risk.
The Challenges Are Real But Not Inevitable
Click image to enlarge, ESC to close.
×
It’s important to acknowledge that the siloed model evolved naturally from organizational structures that predated cloud adoption. CloudOps, security, and compliance were separate disciplines long before multi-cloud was a reality, and the processes built around them reflected a different era of IT.
But the operating environment has changed, and the model needs to change with it.
There is a better approach that treats CloudOps, security, and compliance as parts of one operational foundation rather than three separate disciplines. Security is built into the design process from the beginning. Authorization keeps pace with change instead of relying on periodic reviews. Operations, compliance, and governance work from the same data and share visibility across the lifecycle.
That integrated foundation improves how agencies manage today's multi-cloud environments while preparing them to adopt AI with greater confidence. As we explore in the next blog, building this kind of operating model is practical, achievable, and already happening across government.
Download the Infographic for a quick, visual summary.
Learn more about building the foundation for AI mission success
About the Authors:
Offering Leader, Cloud and Cyber Solutions
Chief Solutions Architect for Cloud Service Delivery
Senior Manager, Cybersecurity Operations